
Claude Code in a Docker Sandbox: How Kits Make It Shareable and Secure
Claude Code sandboxed in a microVM, egress filtered, credentials never entering the VM ~ as a shareable kit. Here's how it works and how to build your own.
Claude Code sandboxed in a microVM, egress filtered, credentials never entering the VM ~ as a shareable kit. Here's how it works and how to build your own.
Docker Sandboxes give AI coding agents a real isolation boundary: a microVM with its own kernel, its own Docker daemon, and a proxy that mediates every outbound request. Most of what makes them genuinely useful isn't on the front page. Here are ten things worth knowing before you run your first one.
Run Docker Agent inside a microVM with one command. Hard VM isolation, workspace-only mount, and API keys that never cross the boundary.
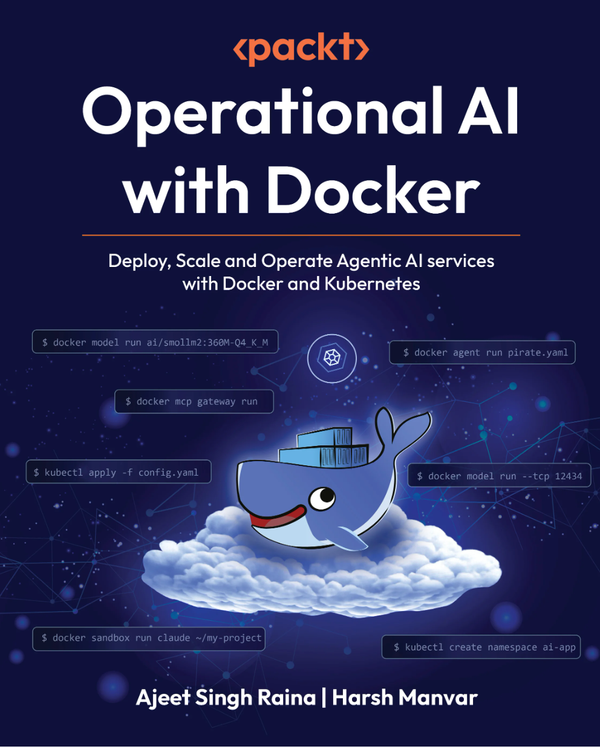
Operational AI with Docker Book is live today. 🎉
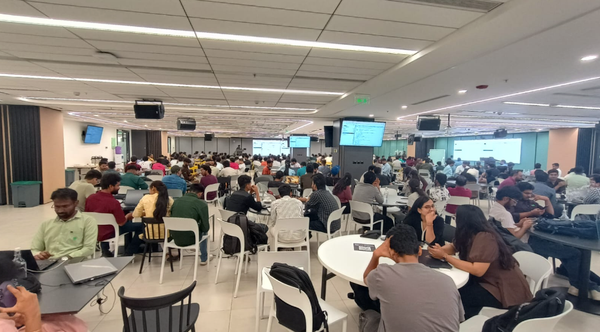
A behind-the-scenes recap of co-organizing the Nemotron 3 Super Meetup at Amadeus Labs, Bengaluru.
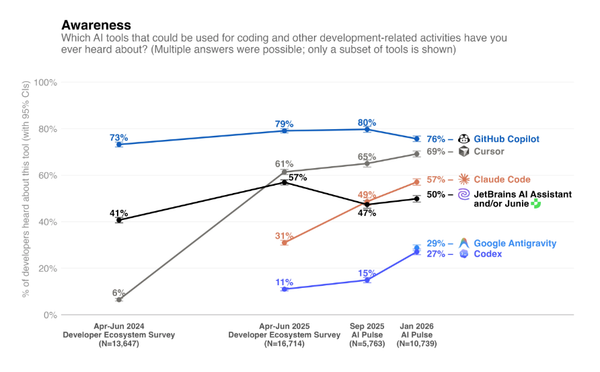
If you spend any amount of time on LinkedIn or X, you already know the feed is saturated with AI coding agents ~ Claude Code, Codex, Gemini CLI, Junie, and a new launch every other week. The hype is loud. The actual adoption inside real engineering teams is harder to read.
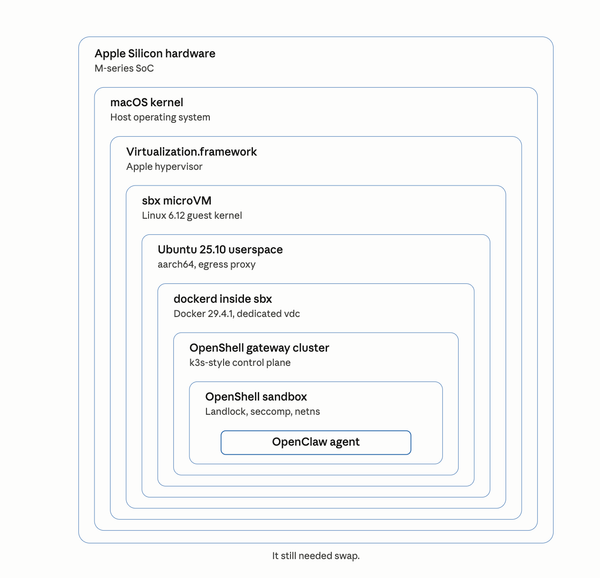
I tried running NVIDIA NemoClaw inside Docker Sandboxes to see what happens when you stack two isolation systems. It got seven layers deep before hitting a wall at /dev/kmsg
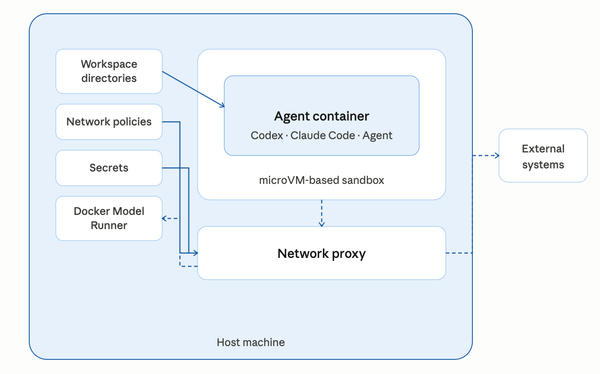
I've been deep in Docker sbx + Docker Model Runner for the past week. The combination is quietly the first real open-source implementation of "agent in a microVM, model on the host, zero cloud." Full walkthrough ~ 8 steps, every command tested on my Mac.
AI coding agents are incredibly useful until you realize they're running next to your SSH keys and AWS credentials. Here's how Docker Sandboxes changes that.
OpenClaw is not safe in its default configuration. With deliberate hardening running inside Docker Sandboxes, keeping it patched, binding the gateway to localhost, and auditing every skill, it becomes conditionally safe for personal use.
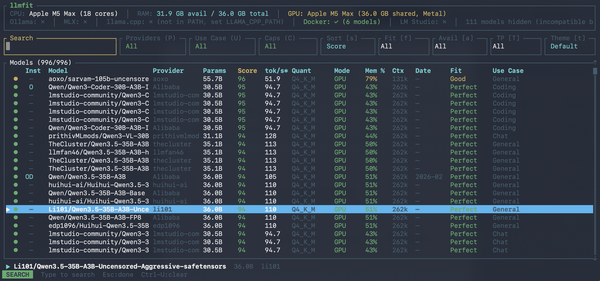
With 21,000+ GitHub stars and 497 models from 133 providers, llmfit is the fastest way to know which local LLMs will actually run and, run well on your machine.
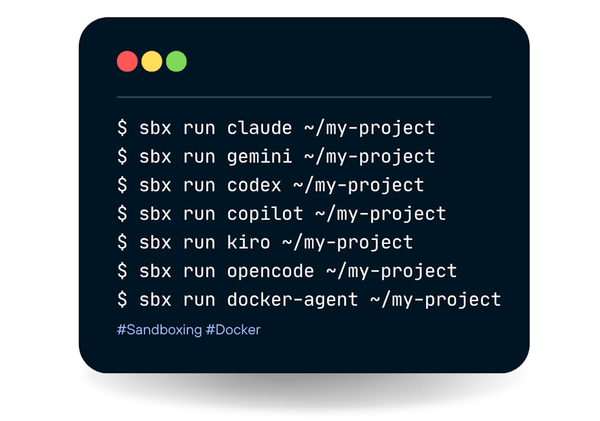
Containers share your host kernel. A container escape gives root on your machine. MicroVMs don't. They give each agent its own kernel, enforced by hardware. Docker sbx is how you run Claude Code, Codex, or any coding agent with full autonomy and zero host risk. Here's exactly how it works.